GitHub and Source Code Recon for Secret Discovery
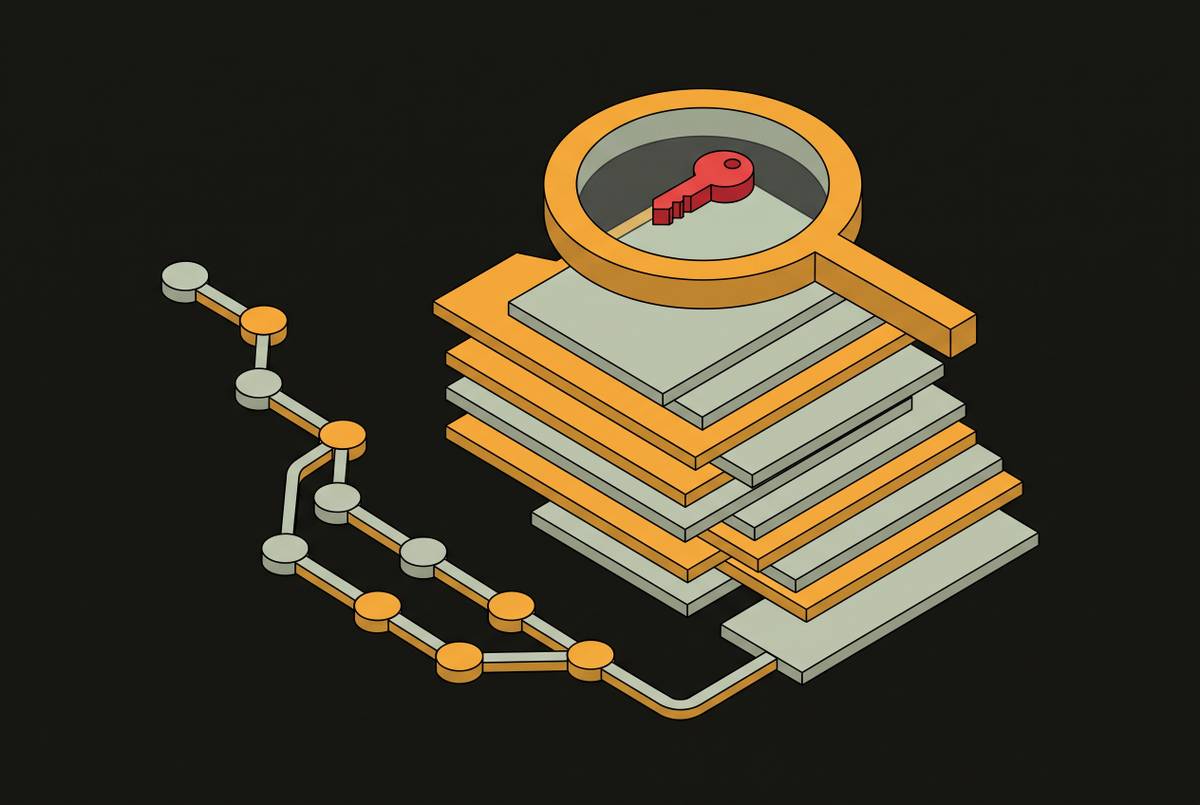
Git's design makes secrets permanent, and attackers know exactly how to find them.
Soren Halvardsen
Git's design makes secrets permanent, and attackers know exactly how to find them.
Hardware-backed security means nothing if developers store secrets in unencrypted databases instead.
Decrypt App Store binaries and extract metadata before diving into raw ARM64 assembly.
Security testers can bypass certificate pinning in minutes using standard tools.
Proxy interception reveals authorization flaws that static analysis cannot catch.
Attackers bypass rate limits through header forgery and GraphQL batching to enumerate data at scale.
Disable gRPC reflection or face automated exposure of your entire attack surface.
Attackers exploit URL parameters to turn your server into a proxy for stealing cloud credentials.
Attackers exploit OAuth's intended features to bypass MFA and steal account access.
Framework convenience features often trade field-level authorization for development speed.
Attackers exploit GraphQL's design defaults to map APIs and bypass rate limits.
Cloud firewalls and load balancers hide services that port scans alone cannot reveal.