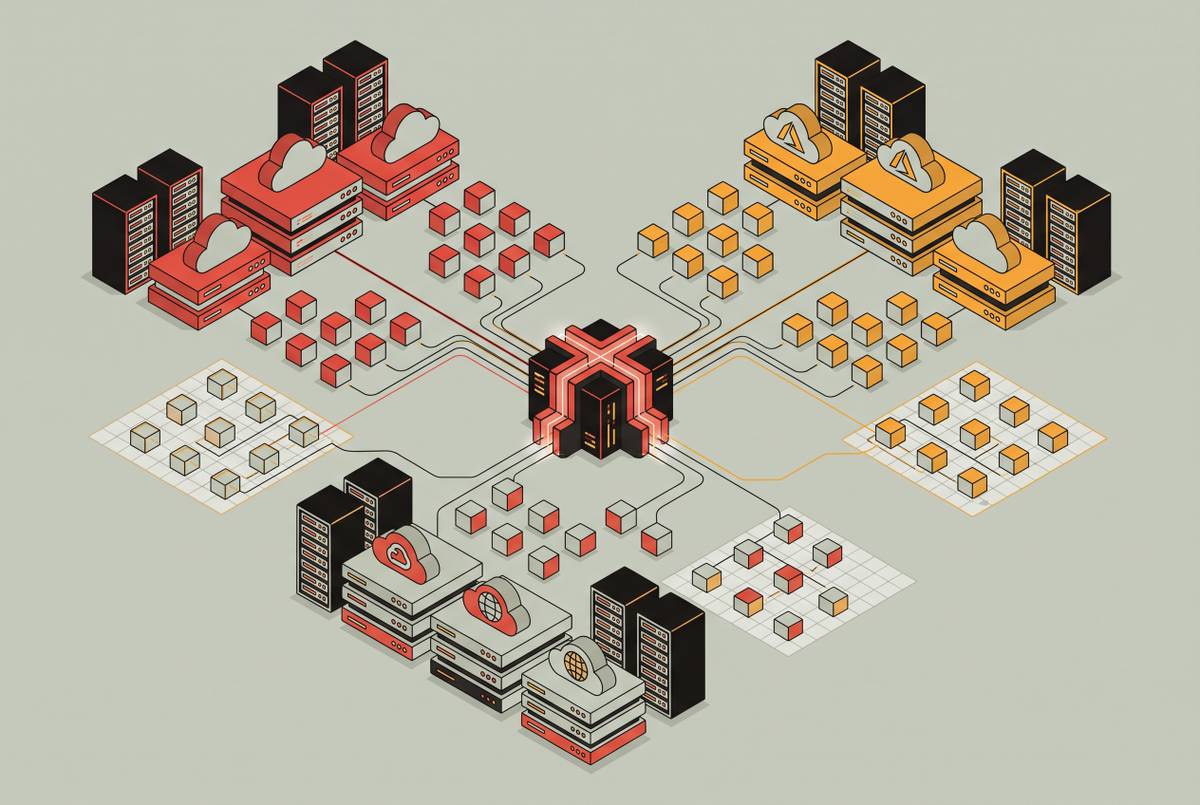
Cloud Asset Discovery in AWS, GCP, and Azure Environments
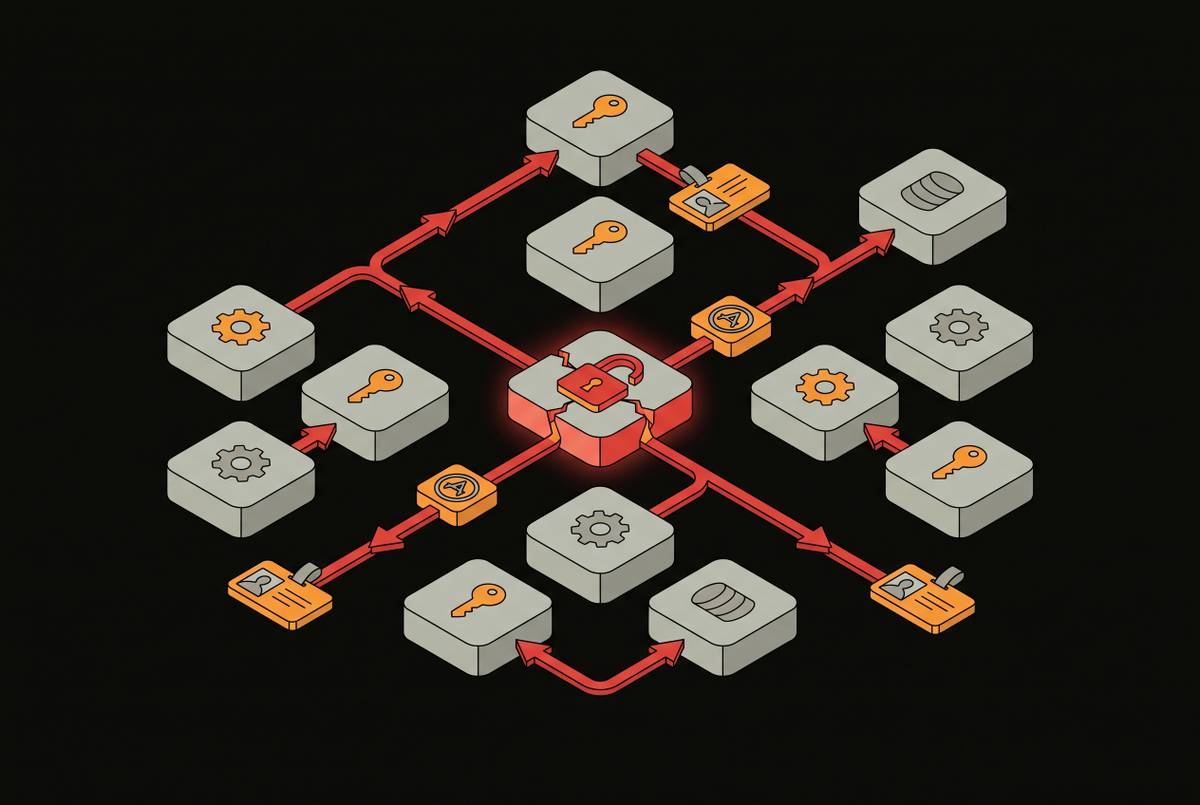
Identity and trust chains, not IP addresses, reveal cloud attack paths.
Deja Okonkwo
Identity and trust chains, not IP addresses, reveal cloud attack paths.
Auditors trace findings through a chain of proof, exploit, and fix confirmation.
Web app tests miss the IAM privilege escalation chains that actually compromise AWS.
Stolen API tokens let attackers hop between SaaS apps undetected.
Shows what attackers could actually steal from your systems, not just theoretical vulnerabilities.
Server-side defenses miss DOM-based XSS because the attack never leaves the browser.
Default XML parsers enable dangerous entity resolution without developers realizing the risk.
A flaw in how JavaScript handles object inheritance can let attackers execute arbitrary code.
A single architectural flaw in multi-tenant systems can expose every customer's data at once.
Stolen credentials open the door, but the exploit chain determines how far an attacker travels.
Modern ORMs don't eliminate SQL injection—developers do when they bypass protections.
Gadget chains in Spring deserialization turn untrusted bytes into remote code execution.