Mass Assignment Vulnerabilities in JSON API Frameworks
Framework convenience features often trade field-level authorization for development speed.
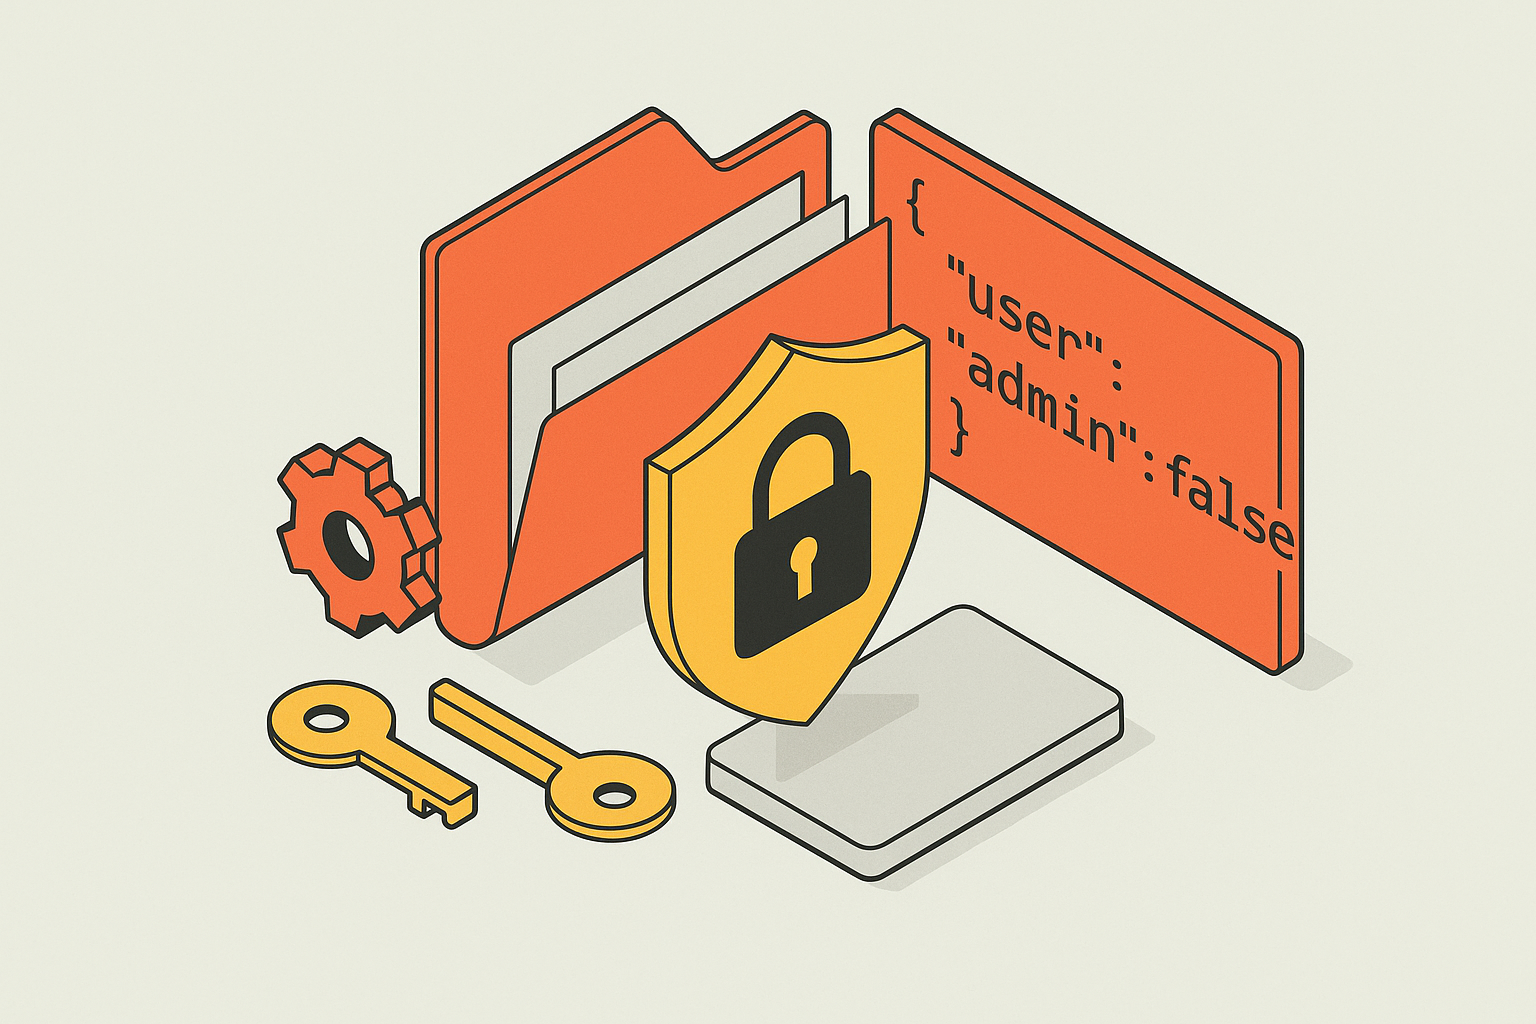
Developers who know what they're doing keep writing APIs with mass assignment in them. The vulnerability isn't a bug born of carelessness. It comes from a framework feature that developers reach for on purpose, because it saves real time and cuts real boilerplate.
Any framework that lets a model bind straight to an incoming JSON body is selling a trade: skip the tedious step of naming every field by hand, and let the framework match request data to model properties automatically. Tutorials teach it this way. Scaffolding tools generate it this way. Startups racing toward a launch date build on it because it works, and because the alternative (writing out field-by-field mappings for every endpoint) looks like wasted effort when a deadline is two weeks out.
The trouble starts with a quiet assumption baked into that convenience: that every field a client is capable of sending is a field the client ought to be allowed to change. That assumption rarely survives contact with a real production model. A user record built for a web form might hold a password and an email, sure, but it might also hold a role, a subscription tier, a verification flag, or an internal balance. None of those belong in the hands of whoever can reach the endpoint. Redbot Security's analysis of the vulnerability class makes a sharp distinction here: a server can correctly confirm that a request comes from a logged-in, authenticated user, while still never checking whether that specific user has permission to change that specific property on that specific object. Authentication answers "who are you." Authorization has to separately answer "what are you allowed to touch," and those are two different checks that a lot of code only half-implements.
That's the opening. The space between endpoint-level authorization and field-level authorization is where mass assignment actually lives, and nothing in a normal request/response cycle flags that the gap exists. A request comes in, the server processes it, a response goes out. Every step looks routine. The rest of this piece is about what happens inside that gap, and what closing it actually takes.
What the attack looks like at the HTTP layer
A mass assignment exploit is a normal, authenticated, properly formatted HTTPS request at the network level, no strange payload, no injection syntax, no malformed packet for a firewall to flag. That plainness is the whole mechanism.
Picture a registration endpoint built to accept a name, an email, and a password. An attacker sends the same POST request a legitimate user would send, except the JSON body carries two extra lines: "role": "admin", or "isAdmin": true. If the backend binds every field in that body to the user model without checking which ones should be writable, the account gets created exactly as the attacker specified it. The server logs a success. The response looks like every other successful registration. Nothing distinguishes this record from a thousand ordinary signups, because at the transport level, nothing is different.
That's why rate limiters, web application firewalls, and TLS inspection miss it. Those tools watch for patterns: too many requests too fast, strings that look like SQL injection, headers that look spoofed. None of them know what a JSON body "should" contain for a given user on a given endpoint, because that knowledge lives in the application's model definitions, not in the traffic. A client sending {"name": "Alex", "email": "a@x.com", "password": "..."} and a client sending the same thing plus "role": "admin", because both are syntactically valid JSON sent over a syntactically valid HTTPS connection to an endpoint the application already exposes.
Attackers don't need to guess blind, either. Field names leak constantly. A GET request on a user resource often returns the full internal model, including fields the frontend never displays. JavaScript bundles shipped to the browser will often name internal properties directly. GraphQL schemas describe every field a type supports, whether or not the UI uses it. API documentation sometimes documents more than it should. And when none of that's available, a short list of common field names (role, isAdmin, admin, price, balance, verified, status, approved, plan, tenantId) covers a wide share of what real production models actually call these properties. Redbot Security's writeup on the pattern makes the point directly: a field doesn't have to appear anywhere in the visible interface to be accepted by the API, if the backend's object binding doesn't check what it's handed. The attacker doesn't need a separate exploit chain or a second system to compromise. The endpoint the application already built for legitimate users is the only tool required.
Mass assignment in four common JSON API frameworks
The underlying pattern stays constant across every framework: a JSON body supplied by the client gets handed directly to a model creation or update call, with nothing filtering out the fields that shouldn't be there. What changes from stack to stack is the syntax that creates the hole. A developer fluent in one framework can walk right past the same mistake written in another language.
In Express applications built on Mongoose, the two telltale forms are User.create(req.body) and Object.assign(existingUser, req.body). Both take the entire request body and apply it to the model, no exceptions. If the User schema includes a role field anywhere in its definition, any caller who slips "role": "admin" into their request body creates themselves an administrator account, full stop on the mechanism, no further trick required. You see these patterns constantly in CRUD generators and in tutorial code that gets copied into real routes under deadline pressure. Finding them in an existing codebase is a matter of searching for the literal patterns: create(req.body, Object.assign(...req.body, and...req.body spread syntax inside the routes directory.
A common serializer auto-generation layer carries its own version of the same risk, because it builds serializer fields straight from the model definition. By default, every field on that model is writable unless a developer explicitly marks it read_only=True. A User model with is_staff, is_superuser, or a groups relationship exposes all three for writing through any serializer that doesn't explicitly lock them down. You can't fix this with a single global setting on the model, because the same model often needs different permission rules on different endpoints. So you need to set read_only_fields inside each serializer's Meta class, or build an explicit allowlist of fields per serializer.
Spring Boot applications built on JPA entities run into trouble when @RequestBody gets applied directly to the entity class. If that entity carries fields like role, enabled, or accountNonLocked, a caller can set every one of them through the same request meant to update a name or an address. The fix is structural: build a dedicated Data Transfer Object that contains only the fields a caller should be allowed to set, and map that DTO onto the entity explicitly inside a service layer. JPA entities should never be the direct target of a @RequestBody parameter. Spring also offers @JsonProperty(access = JsonProperty.Access.READ_ONLY), which marks a field so it gets returned to the client in responses but never accepted from the client in requests.
Ruby on Rails has the longest public history with this vulnerability class, and Rails circles sometimes call it autobinding. In 2012, developer Egor Homakov demonstrated the risk against GitHub itself, using mass assignment to add his own public key to the Ruby on Rails organization and commit directly to the repository. Rails 4 answered with strong parameters, so you now need an explicit permit() call naming every field allowed through before anything reaches a model's create or update call. That protection still gets bypassed in two common ways: calling params.require(:user).permit! (the "permit-bang" form, which opens every field back up), or skipping the strong-parameters layer entirely and passing a raw params hash into the model. Auditing a Rails codebase for this means searching for.permit! directly, and reviewing every create or update call to confirm it routes through a named, explicit strong-parameters method rather than something looser.
What attackers do with unrestricted field binding
Unrestricted field binding is not a theoretical misconfiguration confined to a compliance checklist. Depending on which fields a given model exposes, it opens a direct path to privilege escalation, broken tenant isolation, financial manipulation, or quiet tampering with audit records.
The most direct case is privilege escalation through role flags. Any field named role, isAdmin, is_staff, permissions, or something functionally similar, if bound without restriction, lets any authenticated user promote their own account. CVE-2022-25776, filed against the marketing automation platform Mautic, documented a related failure in that family: logged-in users could reach areas of the application they were never meant to access, exposing sensitive data including names, surnames, and company information.
But the more severe case, by scale of damage, is when tenant isolation collapses inside multi-tenant SaaS platforms. The jshERP case, confirmed in 2026, shows this failure mode at its worst. jshERP ran a shared-database, multi-tenant architecture, with isolation between tenants enforced by a global SQL interceptor. That interceptor treated a tenantId value of 0 as super-admin, applying no filtering. The application's UserService.updateUser function bound the caller's raw JSON body directly onto the User entity, with no field restriction. That combination meant any authenticated user, including someone with access to nothing more than their own sub-user account, could set tenantId: 0 on that account, log back in, and have the interceptor treat the resulting session as an unrestricted super-admin. Those four ordinary-looking API calls gave full read, write, and delete access across every other tenant's business data on the shared instance. Nothing about those four calls would have looked unusual in a request log. Each one matched the shape of a normal update request to an endpoint the application already exposed.
Financial fields follow the same logic on a smaller scale. An order endpoint that accepts a client-supplied price field, a discount endpoint that accepts a raw discountPercent value, or an account endpoint that accepts creditBalance or accountBalance directly, all turn a financial control into whatever number the caller decides to send.
Audit and compliance records carry a quieter version of the same risk. Unrestricted binding can let an attacker overwrite reviewer IDs, approval dates, or audit timestamps, which undermines the reliability of exactly the records that frameworks like SOC 2, HIPAA, and ISO 27001 treat as control requirements. A SaaS company operating under any of those frameworks needs those records to be trustworthy by construction, not by policy.
Recent penetration testing has also found a distinct impact class that produces availability failures instead of data compromise: sending extreme numerical values, such as 1e9 or 1e99999, against an application's id field through mass assignment can disrupt core functions like account creation or invitation handling, breaking the service for everyone rather than exposing data to one attacker.
Spring4Shell showed mass assignment reaching remote code execution
Spring4Shell, tracked as CVE-2022-22965, proved that this vulnerability class can go further than swapping a role flag or inflating an account balance. Under the right conditions, it reaches the most serious outcome in application security: unauthenticated remote code execution.
The mechanism runs through Spring's data binding layer, the same layer responsible for mapping incoming HTTP request parameters onto Java object properties, which is functionally the same job every framework discussed earlier performs with JSON bodies. On JDK 9 and later, an attacker could construct a specially crafted parameter path that walked from a bound object, through its class, to the class loader behind it. From there, manipulating class loader properties let the attacker write a malicious JSP web shell straight to disk.
Exploitation wasn't trivial to pull off at scale. It required an unpatched version of Spring Framework, JDK 9 or later, deployment as a traditional WAR file rather than the embedded-Jar setup most Spring Boot applications default to, and Apache Tomcat specifically as the servlet container. That stack of requirements is why Spring4Shell never produced exploitation at the scale of Log4Shell, despite the severity of the underlying flaw. It still saw real exploitation in the wild: Trend Micro Threat Research confirmed Spring4Shell being used to deploy and run Mirai botnet malware against vulnerable hosts.
Not every mass assignment flaw escalates to code execution. The conditions behind Spring4Shell were specific, so they didn't generalize to most applications running the same pattern. What generalizes is the underlying fact: the data binding layer is a load-bearing security surface central to the real risk. A flaw in how a framework maps request data onto objects can chain into consequences far past the field manipulation that most developers picture when they hear "mass assignment." That's the reason this class deserves the same systematic review as injection flaws or broken authentication, rather than treatment as a minor oversight to fix when time allows.
Finding mass assignment in a live API before an attacker does
Finding mass assignment in a running API requires behavioral testing, not just a scan of traffic patterns or a static code review. The actual test is simple to describe: take every create and update endpoint in the application, add fields that look privileged to the request body, and check whether those fields persist in the resource the API returns.
Reconnaissance comes first: build a list of field names worth testing, starting with a GET request against the target resource, reading every field the response includes, not just the ones a UI happens to display. Response models routinely carry internal fields, role, isAdmin, balance, verified, tenantId, that the update endpoint's own documentation never mentions but will still accept on write. JavaScript bundles shipped to the client, GraphQL schema introspection, published API documentation, and even verbose error messages all tend to reveal more of the underlying model than the visible interface does, and each is worth checking before moving to live testing.
Once a working list of candidate field names exists, the testing itself follows directly: submit each one, individually and in combination, through the same create or update endpoint a normal user would call, and compare the field's value in the stored resource before and after. A field that changes in response to a value it was never supposed to accept has confirmed the vulnerability. Every framework covered here (Express with Mongoose, Django REST Framework, Spring Boot with JPA, and Ruby on Rails) fails this test the same way when binding runs unrestricted. The same behavioral check works regardless of which stack sits underneath the API being reviewed.