Mass Assignment Vulnerabilities in JSON API Frameworks
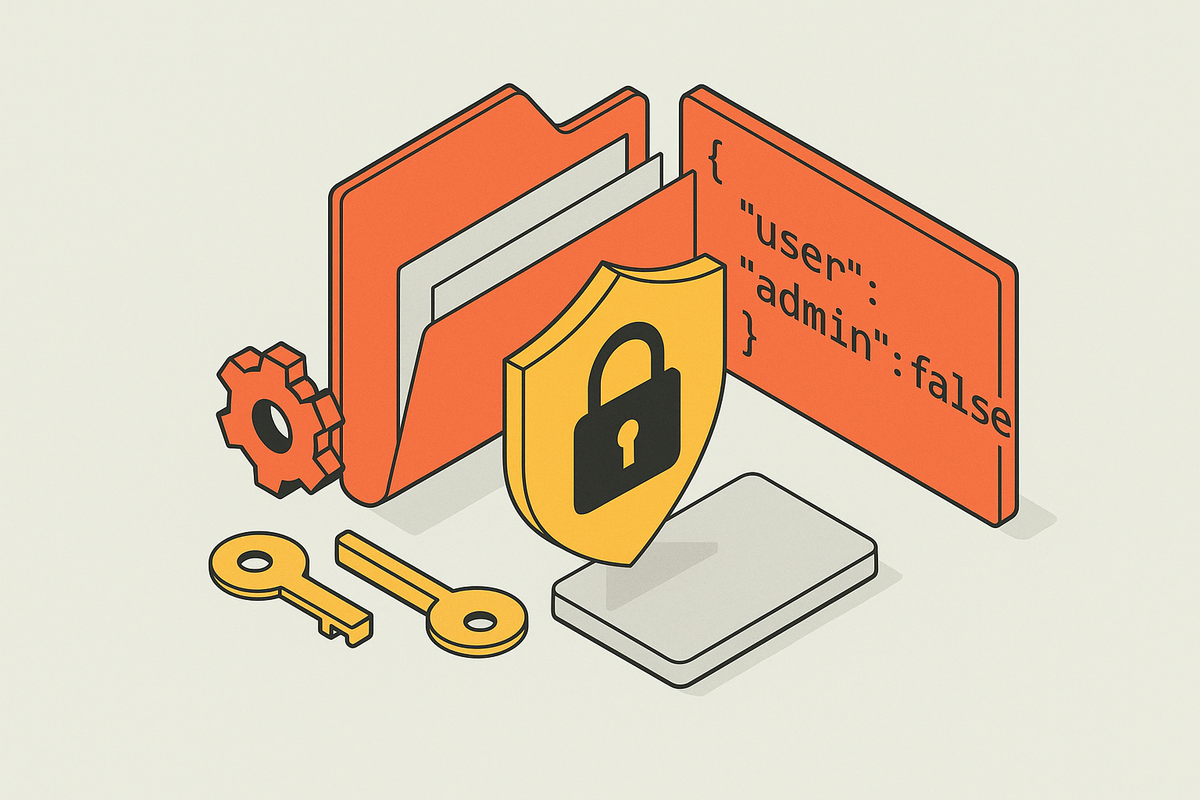
Framework convenience features often trade field-level authorization for development speed.
Priya Nambiar
Staff Writer, Mobile & API Security
Priya holds an offensive security background rooted in mobile application penetration testing, having consulted for fintech startups across Southeast Asia and the UK. Her work focuses on dissecting real-world API misconfigurations and mobile attack surfaces discovered in bug bounty programs.
4 stories
Framework convenience features often trade field-level authorization for development speed.
Attackers exploit GraphQL's design defaults to map APIs and bypass rate limits.
Cloud firewalls and load balancers hide services that port scans alone cannot reveal.
Attackers exploit Java deserialization through gadget chains already present in your dependencies.