Privilege Escalation via Misconfigured Sudo Rules in Linux Environments
Sudo rarely breaks; broad rules, shell-capable binaries, and unpatched flaws hand attackers root.
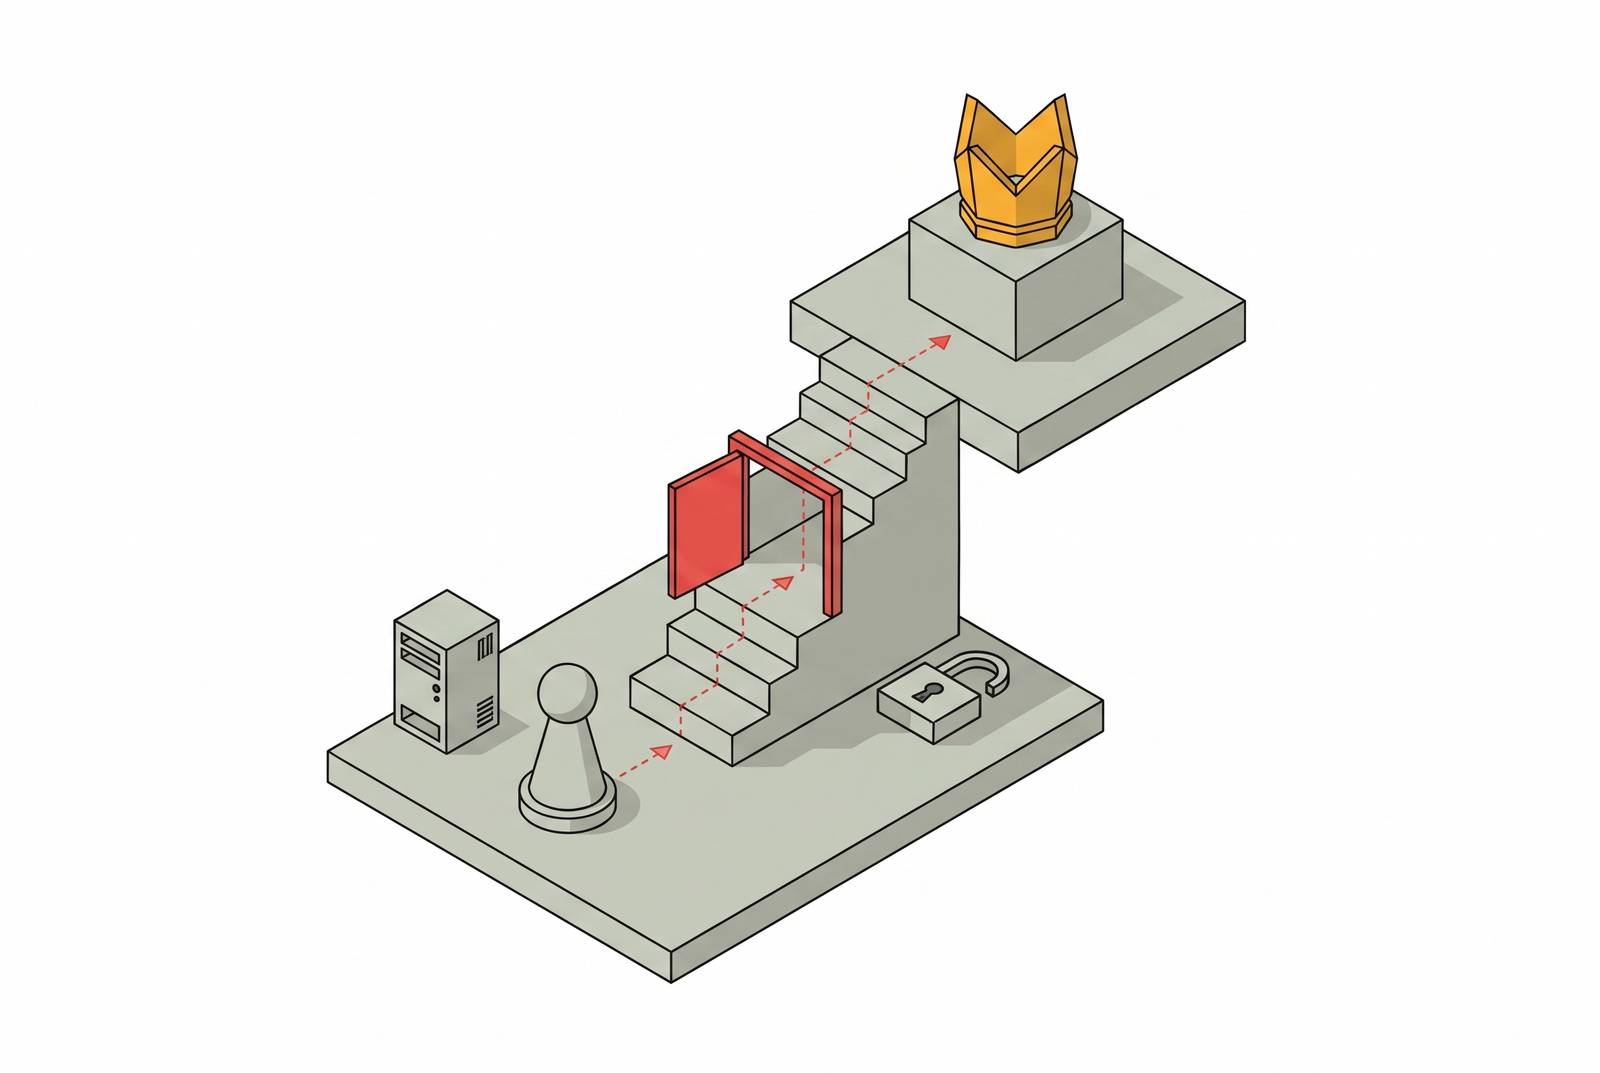
Privilege escalation through misconfigured sudo rules is usually not about breaking Linux. It is about using access that an administrator already granted. Broad passwordless rules, utilities that can launch a shell and unsafe environment settings can let an attacker who has compromised a service account become root. Understanding those paths makes the fix clear, because a safe sudo policy must restrict what a command can actually do.
Why sudo misconfigurations are a local-to-root problem, not a break-in problem
The attacker already controls an account. Linux privilege escalation almost always follows initial access as a low-privilege user, such as www-data, a CI runner or a service account. Sudo then becomes a question of authority. If the policy grants more authority than the account needs, the attacker can use that permission without defeating the system that enforces it.
One compromised account becomes full root access on the host, rather than remaining confined to that account’s work. On a Kubernetes node, the consequences can extend to container escapes, etcd access and lateral movement toward the cluster control plane. The original foothold may be small. The permissions attached to it decide how far the compromise can spread.
What an attacker does first: reading sudo -l and knowing what it means
sudo -l shows which commands the current account can run and which policy settings apply to it. The output is an attack map. A line containing (ALL) NOPASSWD: ALL means the account can run any command as root without a password. A line containing (ALL) NOPASSWD: /usr/bin/vim names one binary instead, but immediately raises the question of whether that binary can launch a shell. GTFOBins is the next reference for that question.
Other lines reveal less obvious openings. (ALL) NOPASSWD: /usr/bin/systemctl * grants unrestricted wildcard arguments, so the named executable does not adequately bound the operation. (ALL, !root) /bin/bash appears to exclude root, but vulnerable sudo versions allow that restriction to be bypassed through CVE-2019-14287. The permitted user, arguments and installed sudo version all affect what the rule allows in practice.
LinPEAS automates this survey and hundreds of additional checks in seconds, color-coding findings by exploitability. Its role is limited to surfacing leads. Manual checks extend the view, with sudo --version identifying the binary version, find / -perm -4000 -type f 2>/dev/null enumerating SUID binaries and getcap -r / 2>/dev/null enumerating capability grants.
NOPASSWD: ALL on service accounts — the most direct path to root
Granting NOPASSWD: ALL to a service account is functionally equivalent to letting that account operate as root. Compromising the account is the only remaining barrier. Once the attacker has a shell, the chain is simply to read sudo -l and execute a command as root. There is no exploit to develop and no CVE to match. Sudo is doing exactly what its policy permits.
The usual justification is that automation needs broad access to work reliably. A tool may need to run some privileged operations without needing to run every privileged operation on the host. The defensive response is to test the minimum command set first, using the tool’s documented least-privilege configuration where available. Skipping that work because a broad grant avoids debugging turns an operational shortcut into a root-access decision.
GTFOBins-exploitable binaries in sudoers — when a named command is still a root shell
Naming an executable can look much safer than granting ALL, even when it gives the account much the same access. The restriction is only as strong as the executable. If a permitted program can start arbitrary subprocesses, those subprocesses can inherit its elevated authority. This is a feature being used as designed. GTFOBins documents how legitimate utilities can cross that boundary.
The shell escapes make the problem concrete. In a sudo-launched vim session, :!sh invokes a shell. A permitted find command can launch one through sudo find . -exec /bin/sh \; -quit, while a permitted Python interpreter can do so through sudo python -c 'import os; os.system("/bin/sh")'. Each route starts with a named utility. The utility then supplies the capability that the sudoers rule appeared to withhold.
Language interpreters such as python, python3, perl and ruby are especially risky because executing other code is part of their purpose. File utilities create related risks, whether through find’s command execution or through tee and cp being able to overwrite sensitive files such as /etc/passwd. A shell is not the only dangerous outcome. For defensive review, a GTFOBins-listed binary should be treated as a root-shell-equivalent grant and removed or replaced with a tightly scoped wrapper that cannot spawn subprocesses.
Environment variable inheritance — how LD_PRELOAD turns a permitted command into arbitrary code execution
Even a suitable command can become unsafe if sudo preserves an attacker-controlled loading environment. The command name is only part of the decision. LD_PRELOAD can cause attacker-controlled code to load into the elevated process, turning permission to run that process into arbitrary code execution. LD_LIBRARY_PATH creates a related risk by redirecting library searches, while PYTHONPATH redirects Python module loading.
The quick policy check is sudo -l | grep LD_PRELOAD. A result showing that the variable is preserved flags an escalation path that a narrow command list does not resolve. The fix belongs in the environment policy. Defaults env_reset, a configured Defaults secure_path and env_keep limited to locale variables address this class of exposure. Command restrictions and environment restrictions must work together because either can undermine the other.
When the sudoers policy is correct but the sudo binary is vulnerable
Policy is not the only layer that can fail. Sudo itself can contain flaws that bypass otherwise sensible rules, and production patching often gives this trusted system binary less urgency than application vulnerabilities. That leaves a separate route to root. Tightening sudoers cannot repair the code responsible for enforcing it.
CVE-2019-14287 shows how an explicit restriction can fail. On sudo versions before 1.8.28, a rule such as (ALL,!root) /bin/bash can be bypassed with sudo -u#-1 /bin/bash. With this special user-ID value, the underlying user-ID calls leave the UID unchanged at 0. The policy appears to forbid precisely the result the attacker obtains. This makes sudo --version an attack-planning step.
CVE-2021-3156, known as Baron Samedit, goes further. The heap buffer overflow in sudoedit -s affects sudo 1.8.2–1.8.31p2 and 1.9.0–1.9.5p1, and requires no sudoers rights at all. The official sudo advisory states that a local user can reach root even when not listed in sudoers, without user authentication. The vulnerable binary is enough.
Stratascale Cyber Research Unit discovered CVE-2025-32463, disclosed June 30, 2025, with a CVSS score of 9.3. It affects sudo 1.9.14 through 1.9.17. The flaw applies the --chroot operation before verifying user permissions, allowing a malicious /etc/nsswitch.conf in a user-controlled chroot directory to cause a rogue shared library to load with root privileges. CISA added the vulnerability to its KEV catalog after evidence of active exploitation. This was not just a theoretical bypass.
The related CVE-2025-32462, disclosed at the same time with a CVSS score of 2.8, concerns sudo’s -h host option. It can let a user claim permissions held on another host in a shared sudoers environment, with particular consequences for LDAP-backed rules. Its affected feature went undetected for over 12 years, while the chroot flaw remained undiscovered for about two years. Trusted code is not automatically well-scrutinized code.
Custom scripts invoked through sudo — the misconfiguration hiding inside the grant
A custom script can hide the same breadth of access behind a reassuringly specific name. Sudo authorizes the script, but the script decides what happens next. Relative binary calls, writable paths and temp-file races can therefore inherit root privileges from an apparently narrow grant. Reviewing only the sudoers line leaves that gap untouched.
For example, a script that calls tar or python without a hardcoded path may rely on the invoking user’s PATH. If that environment is inherited and a searched directory is user-writable, an attacker can plant a replacement executable with the expected name. The script then runs the substitute as root. This is PATH injection, which ties how a script is written to the environment controls discussed earlier.
Even a script that is not writable can be replaced if its parent directory is world-writable. The audit therefore has to include the script’s location, dependencies and contents. SUID and other privilege-granting file permissions belong in the same review pass because they also grant elevated authority outside ordinary account permissions.
What detection looks like — and why sudo misconfigs are usually found by attackers before defenders
These paths often produce little noise because they use normal commands and need no anomalous network traffic. The attacker is using an approved mechanism. That makes these paths easy to find from a compromised shell and makes abuse hard to tell apart from an administrator’s work.
sudo -l illustrates the problem. A competent engineer may run it on an unfamiliar host, and an attacker may run it immediately after gaining access. The command line alone cannot reliably distinguish those cases. What follows is more useful, such as a GTFOBins-style subprocess launched from a sudoed editor or interpreter. Detection needs to take that behavior into account while allowing for permission checks that are harmless.
Centralized sudo logging, auditd and behavioral awareness provide complementary parts of that context. None closes the gap alone, and environments commonly lack a properly configured combination. The presence of pspy is another signal to watch for because it tracks which processes run without needing root privileges, revealing activity such as hidden cron jobs. On a host, it can indicate active privilege-escalation reconnaissance. That signal still needs to be assessed with care before drawing conclusions about each process seen.
Hardening sudoers — the specific controls that close each attack path
The defensive response is to close each route at the layer where it originates. Remove NOPASSWD: ALL and replace it with the minimum commands a service account actually requires, using explicit absolute paths and no wildcard arguments. Remove GTFOBins-listed binaries from sudoers. Where a utility remains necessary, replace the direct grant with a wrapper that performs only the intended operation and cannot spawn subprocesses. That wrapper needs its own review for unsafe paths and file replacement.
Environment and binary controls address different failures. Enforce Defaults env_reset, configure Defaults secure_path and limit env_keep to locale variables to block unsafe inheritance and PATH hijacking. Patch sudo to the current release. Both CVE-2025-32463 and CVE-2025-32462 are fixed in sudo 1.9.17p1. Unpatched systems running 1.9.14 through 1.9.17 remain exposed to the chroot escalation path regardless of how carefully sudoers is written.
Configure Defaults logfile="/var/log/sudo.log" and enable Defaults log_input, log_output, then ship sudo logs to a SIEM before an attacker with root can clear them. Apply file integrity monitoring to /etc/sudoers and /etc/sudoers.d/ to detect unauthorized additions, with these controls complementing the behavioral detection described earlier. They do not substitute for removing dangerous grants.
Tighter restrictions do create operational friction. Package management, device access, service startup and backup tooling can legitimately require specific elevated permissions, so blanket removal is not the answer. Exceptions need owners and explicit review cycles. Because new vulnerabilities can undermine policies that were sound when written, sudo review belongs in a recurring security program. The durable judgment is to examine what each grant enables as commands, scripts and the sudo binary change.