Writing Audit-Ready Penetration Test Findings
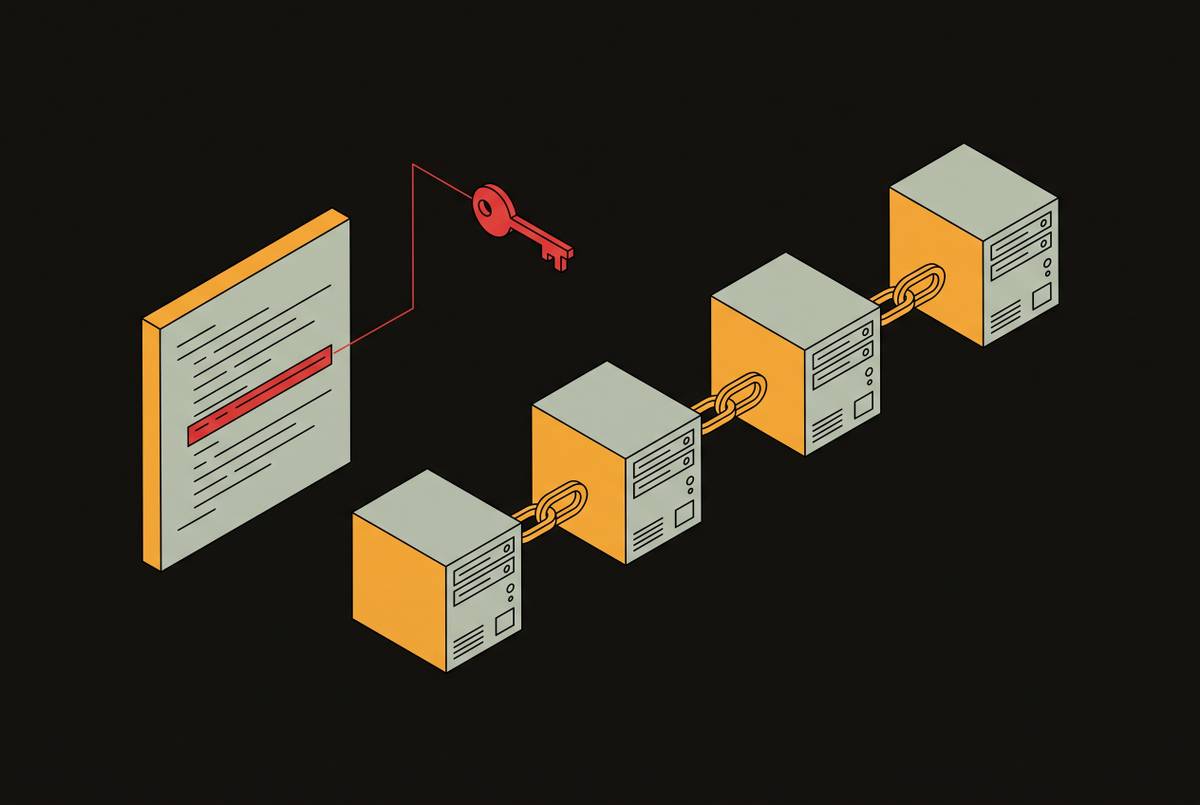
Auditors trace findings through a chain of proof, exploit, and fix confirmation.
Marcus Yuen-Castillo
Contributing Researcher
Marcus worked as a network penetration tester and malware analyst for a mid-sized managed security provider for nearly a decade before shifting his focus to writing long-form technical research. His pieces tend to examine post-compromise tradecraft and the overlap between automated exploitation tools and hands-on-keyboard techniques.
5 stories
Auditors trace findings through a chain of proof, exploit, and fix confirmation.
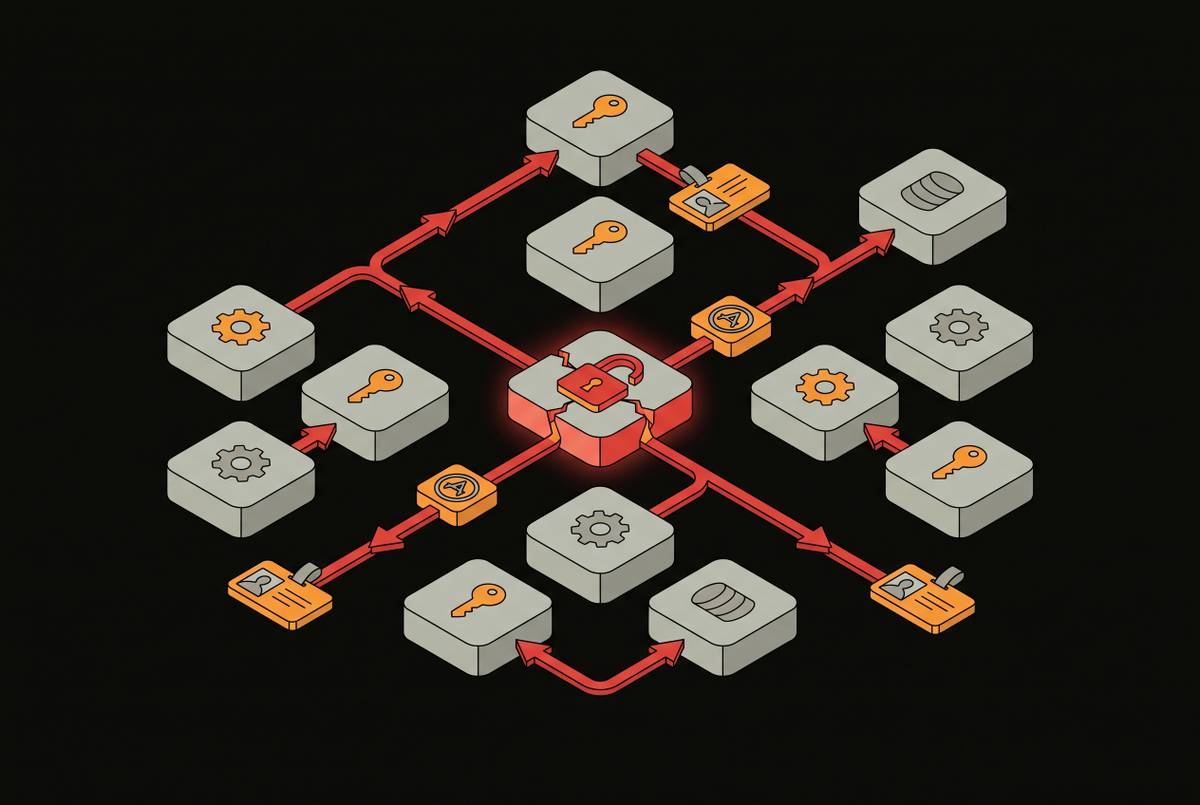
Stolen API tokens let attackers hop between SaaS apps undetected.
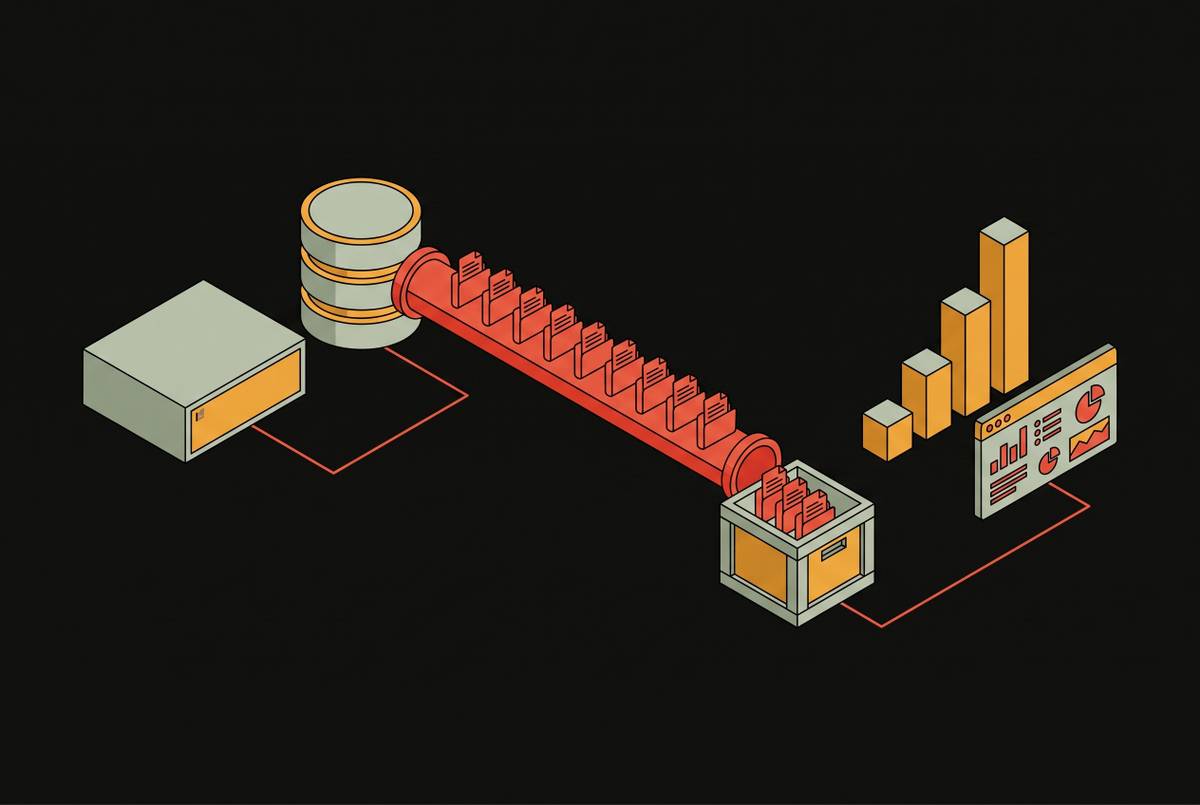
Shows what attackers could actually steal from your systems, not just theoretical vulnerabilities.
Stolen credentials open the door, but the exploit chain determines how far an attacker travels.
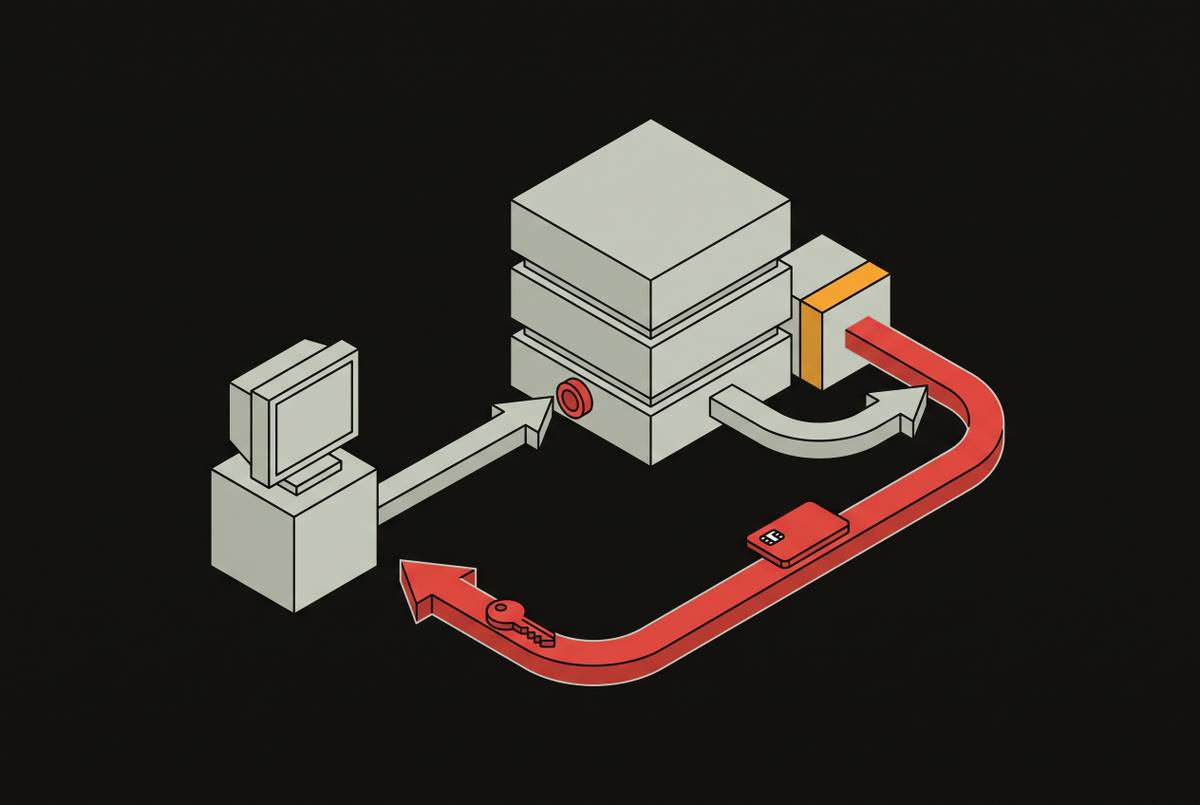
Attackers chain SSRF into AWS metadata endpoints to steal credentials in just three HTTP requests.